The Rsa Cryptosystem Ideas Practical Cryptography For Developers
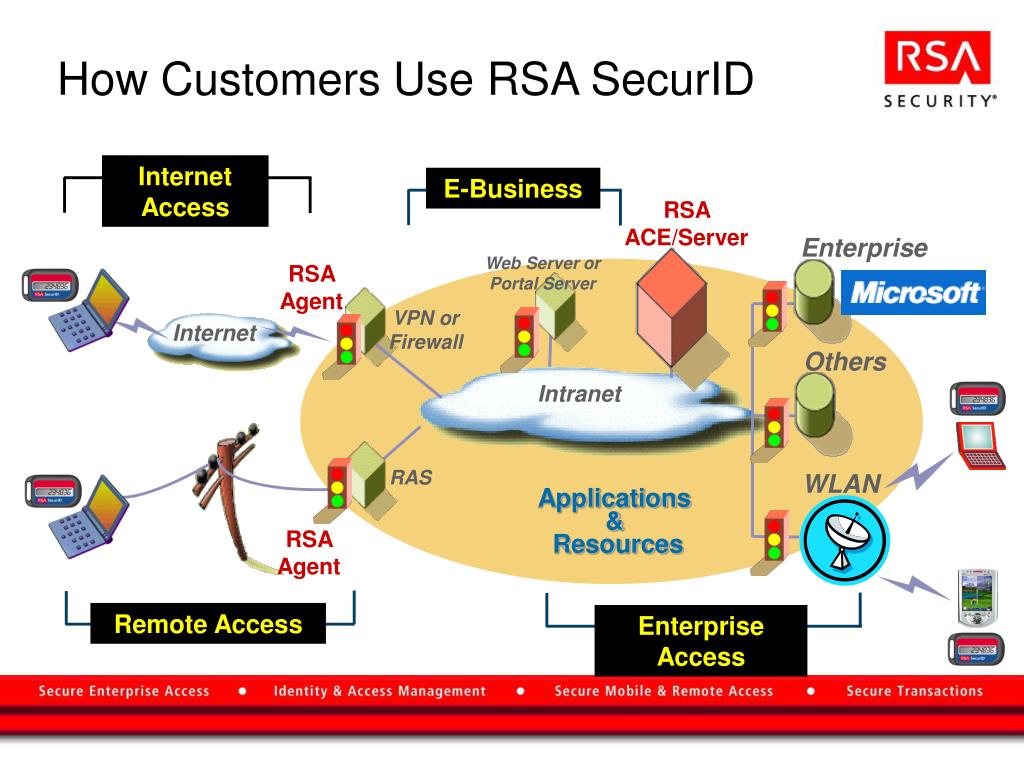
These are the risks that demand organizations’ quick consideration, action, and funding. Since its founding, RSA Safety has helped organizations defend themselves from phishing, malware, social engineering, and different recurring risk vectors. RSA is constant to innovate against emerging threats like deepfakes, AI-powered assaults, and IT Help Desk bypasses.
Textual Content Dimension
We will choose SHA-1 as a hash perform in OAEP and \(hLen\) denotes the length in octets of the hash operate output. We will later demonstrate why even MD5 or SHA-1 is a secure choice for OAEP even when it’s not collision resistant. Any RSA key the place \(d\) is bigger than \(λ(n)\) is considered non-compliant in those strict contexts. This effectively forces implementations to make use of the smaller \(λ(n)\)-based exponent, since any “oversized” \(d\) can be decreased \(mod ~~λ(n)\) to meet the criterion. To completely recognize this reality, let’s take a step back to grasp why the size of the private exponent \(d\) matters in RSA. This can later be verified by others utilizing the corresponding public key.
These benefits make elliptic-curve-based variants of encryption scheme extremely engaging for utility the place computing sources are constrained. Elliptic Curve Cryptography (ECC) is a term used to describe a collection of cryptographic tools and protocols whose safety relies on special variations of the discrete logarithm problem. Bigger composite numbers are easy to make and astronomically more durable https://sportsbookpayperhead.com/tag/cybersecurity/ to factor.
- Truly, because the World Wide Internet has turn into a world phenomenon, there has been an rising need for more alphabets and even writing systems (like Chinese) which don’t use alphabets.
- In RSA, the basic public key’s used for encryption and signature verification, while the private secret is used for decryption and signing.
- At All Times use high-entropy sources when generating RSA keys to keep away from compromised keys.
- It’s necessary to note that whereas OAEP and PSS enhance the security of RSA in opposition to classical attacks, they do not shield RSA from quantum attacks.
- This masks is applied both to the info block \(DB\) and to the random seed used in the encoding process.
If both of these two capabilities are proved non one-way, then RSA might be damaged. In reality, if a way for factoring efficiently is developed then RSA will no longer be protected. (For ease of understanding, the primes p & q taken listed below are small values. Virtually, these values are very high). Actually, as the World Broad Web has turn out to be a global phenomenon, there was an rising need for more alphabets and even writing systems (like Chinese) which do not use alphabets.
We will use a salt, \(S\), randomly generated string of mounted size (often the same as \(hLen\)). This randomness is important in guaranteeing that every signature is exclusive, even for the same message. The leading \(0x00\) byte ensures that when \(EM\) is interpreted as an integer, it’s less than the RSA modulus \(N\). At this level, \(EM\) is your OAEP-padded message of length \(k\). Form the padding string \(PS\), the size of \(PS\) is chosen so that the entire block \(DB\) has length \((k−hLen−1)\) bytes.
Public Key Encryption
RSA’s security relies on the difficulty for computer systems to search out https://life-connected.com/floridas-well-being-division-undercounted-covid-19-circumstances-deaths-because-of-technical-points-state-audit.html the prime numbers in the encryption keys. While 1024-bit keys were once considered safe, the rising computing power has led to a shift in course of 2048-bit keys. The alternative of padding scheme is determined by the particular utility and safety necessities.
When Not To Use Rsa Encryption
This means \(λ(n)\) provides the minimal exponent needed for RSA’s correctness, whereas \(φ(n)\)might be a bigger quantity that still works but isn’t needed. The yr 1978 witnessed the start of a brand new era in cryptography with the introduction of the RSA cryptosystem, named after its inventors (Rivest, Shamir, and Adleman). These characters represent two events engaged in communication, with Alice sometimes representing the sender or initiator, and Bob representing the receiver or responder.
Numerically, \(PS\) has \((k−mLen−2⋅hLen−2)\) bytes of \(0x00\), where \(mLen\) is the length of the message \(M\). We may even use a Mask Generation Perform, \(MGF\), which is often mentioned as \(MGF1\). This function takes an input (seed or masked data) and produces an output of a specified length by iterating the underlying hash operate. We’ll write \(MGF(input,length)\) to point “generate a masks of \(length\) bytes from \(input\)”. Optimum Asymmetric Encryption Padding requires a hash perform for two operations we’ll focus on in this part.
And because the world approaches a model new quantum computing era, RSA is continuing to innovate to help organizations keep forward of dangerous actors. RSA keys can be usually 1024 or 2048 bits lengthy, but specialists believe that 1024-bit keys could be damaged shortly. ElGamal cryptosystem, called Elliptic Curve Variant, relies on the Discrete Logarithm Downside. It derives the strength from the belief that the discrete logarithms cannot be present in practical time-frame for a given quantity, while the inverse operation of the power could be computed effectively. Subsequently, the perform which multiplies two massive primes together to get a very massive composite is a good candidate for a cryptographic one-way function.
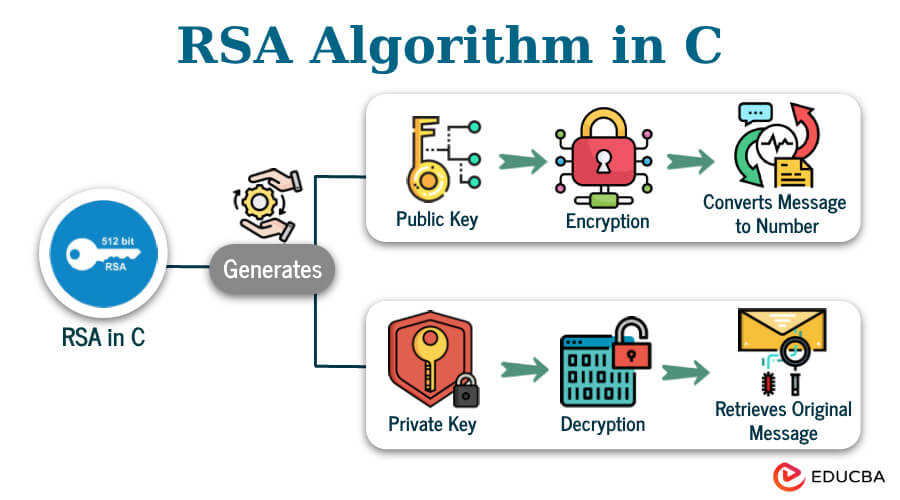
This provides a secure method of communication over public networks, as anybody can use the public key to encrypt a message, however only the recipient can decrypt it utilizing their personal key. When creating virtual signatures, the sender first generates a hash price for the message the usage of a cryptographic hash operate. RSA is predicated on the problem of breaking down large numbers into their top factors. To create an RSA key pair, you want to decide very huge prime numbers, p and q. It is crucial to choose these primes randomly and guarantee they are simply distinctive from every different.